CPLANE helps plants and the system integrators who serve them put cybersecurity in the control layer. Built to IEC 62443. A February 2026 U.S. Army red team found no vulnerabilities that allowed unauthorized access to control.
Exposed controllers and a single-vendor stack leave the plant with one path for both operations and security. A patch still waits on the vendor's window.
The control layer is built to IEC 62443-4-2 SL2. Zoning, access, and the response to a security event sit in the architecture.
Talk with an ExpertSecurity designed into the control layer, then proven on one unit.
Controller inventory, where remote access lives, and which units cannot take an unplanned outage.
Live control starts on one isolatable unit. The rest stays on the installed stack until that unit proves itself.
CPLANE does not go around the SI who already knows the plant. Engineering, the integrator, and operations stay in the loop.
Validate the platform on the Fusion 500 before a wider rollout. Same IEC 62443 control layer as production.
The control layer, built to IEC 62443. One open control architecture.
Controllers, remote access, and the path between the enterprise network and the control network.
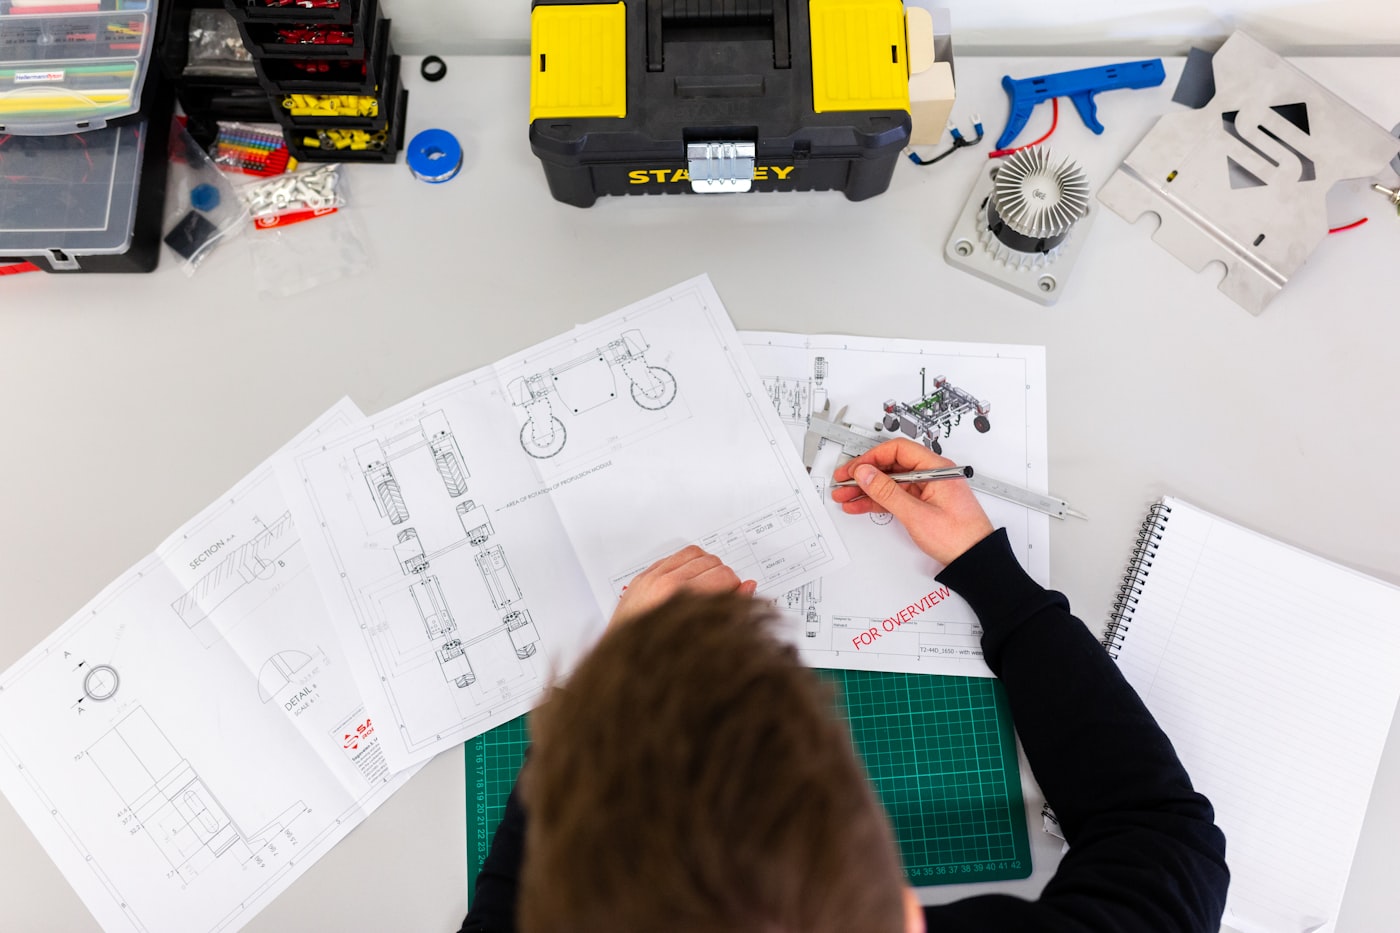
When security is added after the controller is installed, the plant still depends on that vendor for the patch and the outage.
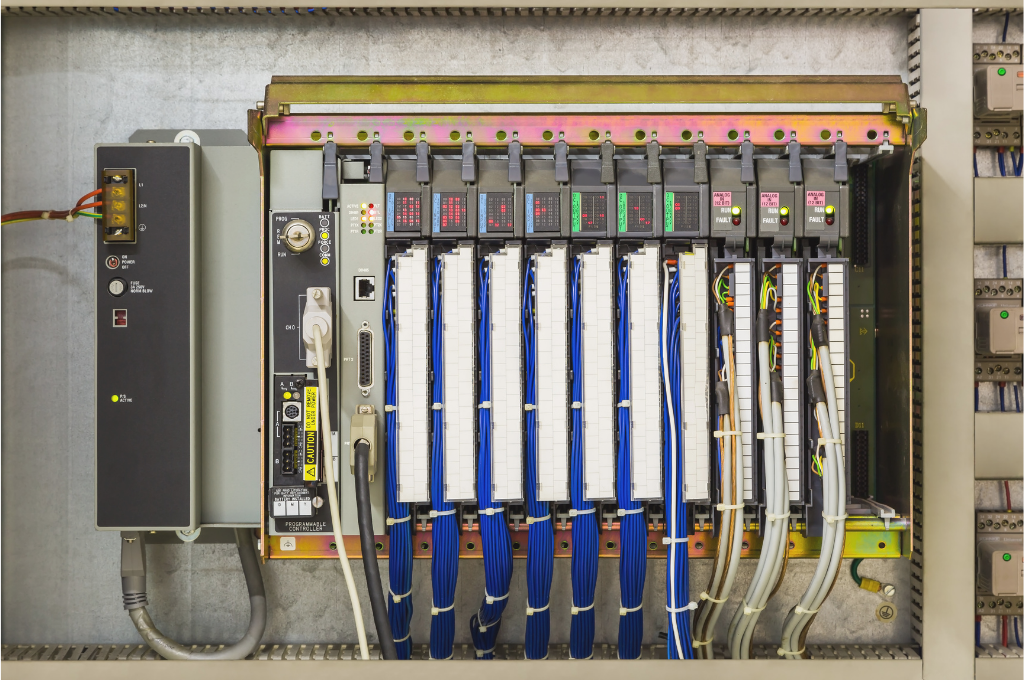
Zoning and access are part of the control architecture. The plant can move one unit at a time.
Harder to attack, easier to patch, cheaper to sustain, and free of single-vendor dependency at every layer. Software failover in under one control cycle. No extra standby chassis.

The control layer is built to IEC 62443-4-2 SL2. A February 2026 U.S. Army red team found no vulnerabilities that allowed unauthorized access to control.
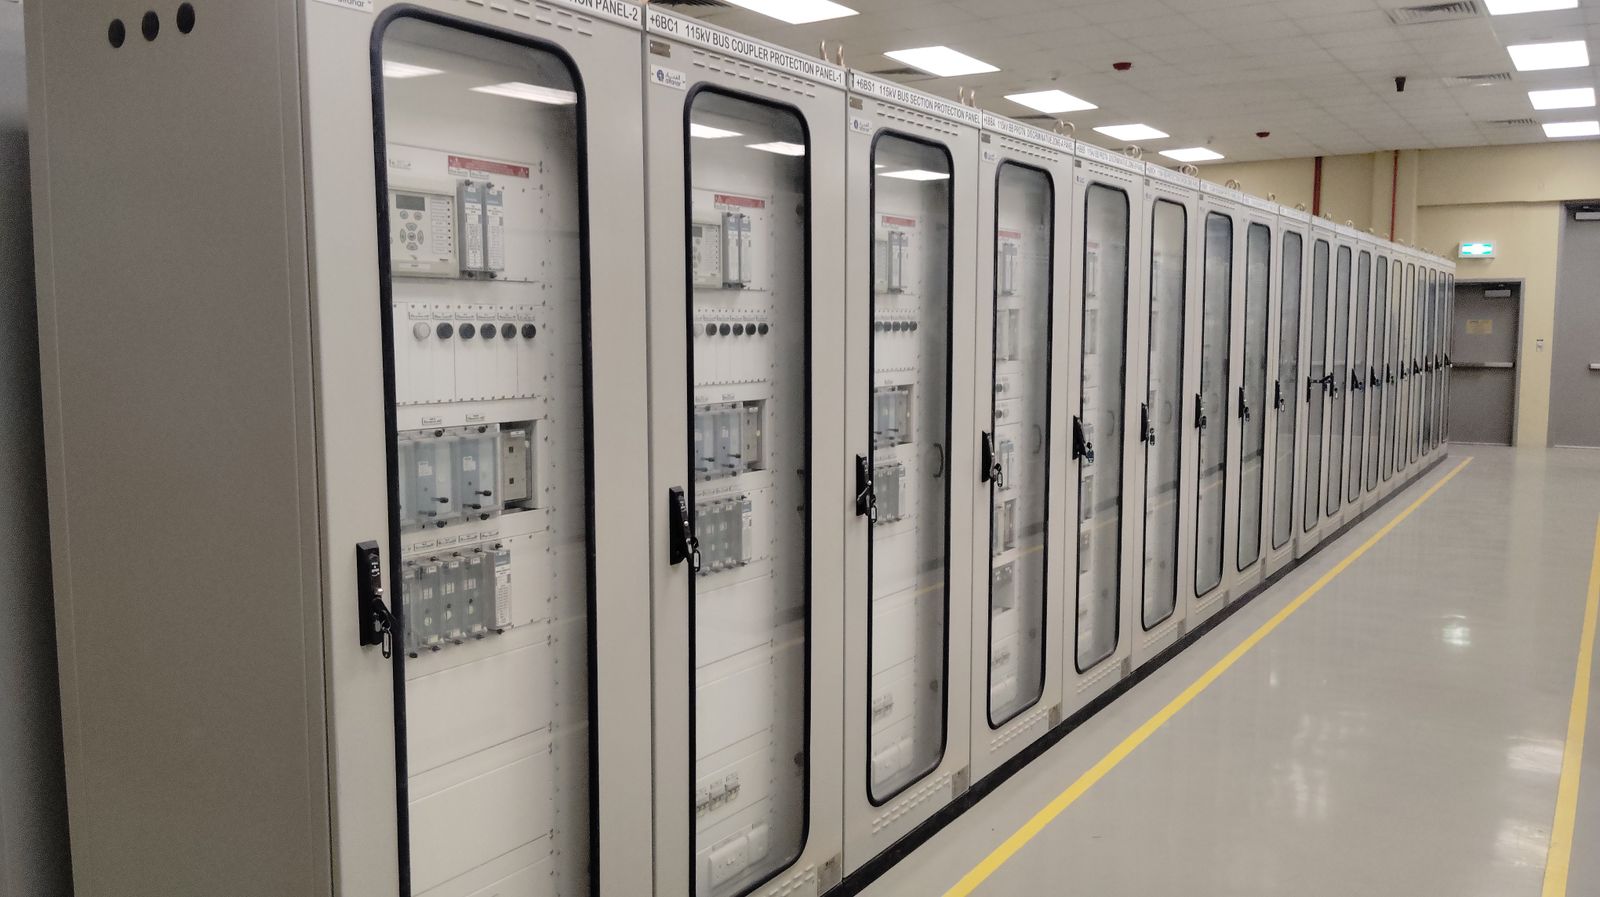
Open control on this stack is in production at an ExxonMobil chemical terminal, a continuous process that stays online. Fusion 500 is the evaluation unit before a wider rollout.
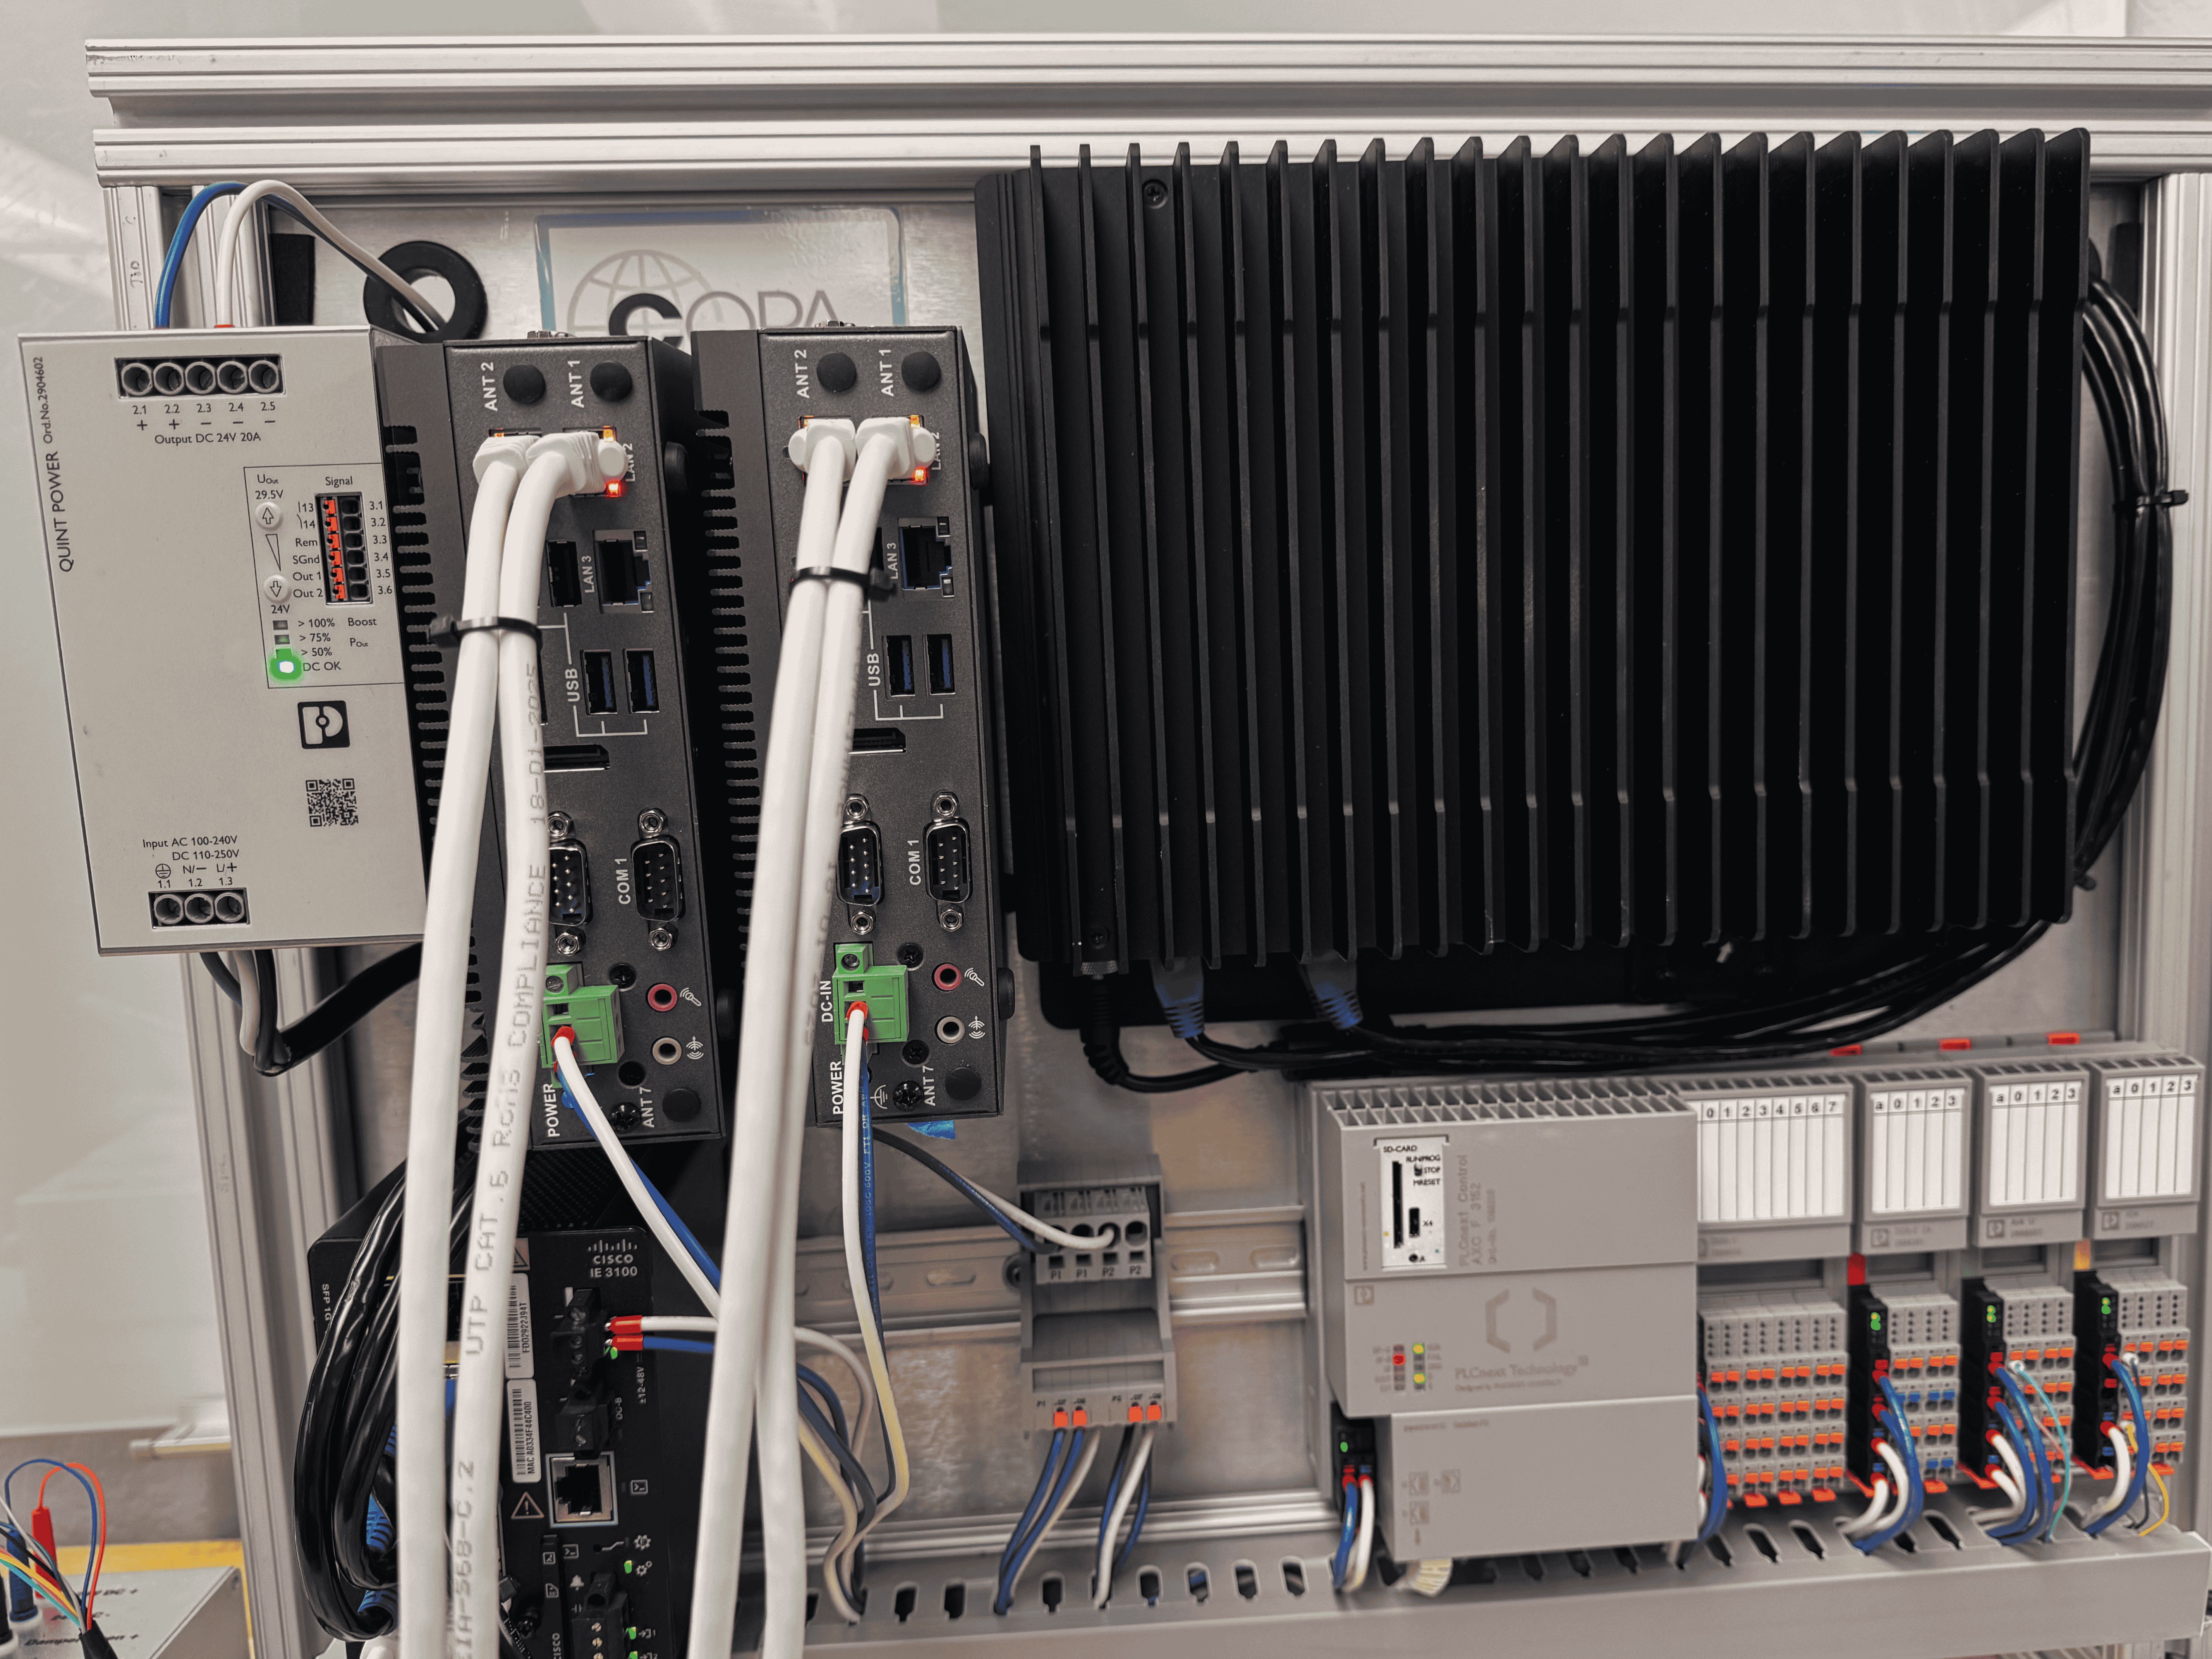
Built to IEC 62443-4-2 SL2.
A February 2026 U.S. Army red team found no vulnerabilities that allowed unauthorized access to control.